Nym Node Configuration
Our documentation often refers to syntax annotated in <> brackets. We use this expression for variables that are unique to each user (like path, local moniker, versions et cetera).
Any syntax in <> brackets needs to be substituted with your correct name or version, without the <> brackets. If you are unsure, please check our table of essential parameters and variables .
Basic Changes
Nym Node can be configured directly by editing the config file (config.toml) located at ~/.nym/nym-nodes/<ID>/config/config.toml (by default ~/.nym/nym-nodes/default-nym-node/config/config.toml) or through commands on the binary.
Node Description
Operators can add a description themselves to share more information about their nym-node publicly.
To add or change nym-node description is done by editing description.toml file located in ~/.nym/nym-nodes/<ID>/data/description.toml. After saving, don’t forget to reload and restart your node service or simply restart your nym-node if you run it without a service (not recommended).
Query description
Nodes description can be queried from API endpoint /api/v1/description or via Swagger API UI page /api/v1/swagger/#/Node/description.
curl -X 'GET' \
  'http://<PUBLIC_IP>:8080/api/v1/description' \
  -H 'accept: application/json'

# or for https reversed proxy or WSS setup
curl -X 'GET' \
  'https://<HOSTNAME>/api/v1/description' \
  -H 'accept: application/json'
Commands & Examples
Disable sharing of system hardware info with the network:
./nym-node run --id <ID> --deny-init --mode entry-gateway -w --expose-system-hardware false --expose-system-info falseAlternatively these values can be changed in config.toml of your node. After saving, don’t forget to reload and restart your node service or simply restart your nym-node if you run it without a service (not recommended).
Note:
--expose-system-info falsesupersedes--expose-system-hardware false. If both are present with conflicting values, the system hardware will not be shown.
VPS Setup and Automation
Replace
<NODE>variable with type of node you run, in majority of cases this will benym-node(depreciatednym-mixnode,nym-gatewayornym-network-requesterare no longer supported).
Although it’s not totally necessary, it’s useful to have nym-node automatically start at system boot time. We recommend to run your remote operation via tmux for easier management and a handy return to your previous session. For full automation, including a failed node auto-restart and ulimit setup, systemd is a recommended choice for all operators, as it allows much more automation leading to better uptime and performance.
Do any of these steps and run your automated node before you start bonding process!
nohup
nohup is a command with which your terminal is told to ignore the HUP or ‘hangup’ signal. This will stop the node process ending if you kill your session.
nohup ./<NODE> run <ARGUMENTS> # use all the flags you use to run your nodetmux
One way is to use tmux shell on top of your current VPS terminal. Tmux is a terminal multiplexer, it allows you to create several terminal windows and panes from a single terminal. Processes started in tmux keep running after closing the terminal as long as the given tmux window was not terminated.
Use the following command to get tmux.
| Platform | Install Command |
|---|---|
| Arch Linux | pacman -S tmux |
| Debian or Ubuntu | apt install tmux |
| Fedora | dnf install tmux |
| RHEL or CentOS | yum install tmux |
| macOS (using Homebrew | brew install tmux |
| macOS (using MacPorts) | port install tmux |
| openSUSE | zypper install tmux |
In case it didn’t work for your distribution, see how to build tmux from version control .
Running tmux
Now you have installed tmux on your VPS, let’s run a Mix Node on tmux, which allows you to detach your terminal and let your <NODE> run on its own on the VPS.
- Pause your
<NODE> - Start tmux with the command
tmux- tmux terminal should open in the same working directory, just the layout changed into tmux default layout.
- Start the
<NODE>again with a command:
./<NODE> run <ARGUMENTS> # use all the flags you use to run your node- Now, without closing the tmux window, you can close the whole terminal and the
<NODE>(and any other process running in tmux) will stay active. - Next time just start your teminal, ssh into the VPS and run the following command to attach back to your previous session:
tmux attach-session- To see keybinding options of tmux press
ctrl+band after 1 second?
systemd
Create a service file
To automate with systemd use this init service file by saving it as /etc/systemd/system/nym-node.service and follow the next steps.
- Open service file in a text editor
nano /etc/systemd/system/nym-node.service- Paste this config file, substitute
<USER>and<PATH>with your correct values and add all flags to run yournym-nodetoExecStartline instead of<ARGUMENTS>:
[Unit]
Description=Nym Node
StartLimitInterval=350
StartLimitBurst=10

[Service]
User=<USER>
LimitNOFILE=65536
ExecStart=<PATH>/nym-node run <ARGUMENTS> # add all the flags you use to run your node
KillSignal=SIGINT
Restart=on-failure
RestartSec=30

[Install]
WantedBy=multi-user.targetAccepting T&Cs is done via a flag --accept-operator-terms-and-conditions added explicitly to nym-node run command every time. If you use systemd automation, add the flag to your service file’s ExecStart line.
- Save config and exit
Make sure your ExecStart <PATH> and run command <ARGUMENTS> are correct!
Example: If you have built nym in the $HOME directory on your server, your username is jetpanther, and node <ID> is puma, then the ExecStart line (command) in the script located in /etc/systemd/system/nym-node.service for might look like this:
ExecStart=/home/jetpanther/nym/target/release/nym-node run --id puma.
Basically, you want the full path to nym-node. If you are unsure about your <PATH>, then cd to your directory where you run your <NODE> from and run pwd command which returns the full path for you.
Following steps for nym-node running as systemd service
Once your service file is saved follow these steps.
- Reload systemctl to pickup the new unit file:
systemctl daemon-reload- Enable the newly created service:
systemctl enable nym-node.service- Start your
<NODE>as asystemdservice:
service nym-node startThis will cause your <NODE> to start at system boot time. If you restart your machine, your <NODE> will come back up automatically.
Useful systemd commands for easier management
- You can monitor system logs of your node by running:
journalctl -u nym-node -f- Or check service status by running:
systemctl status nym-node.service
# for example systemctl status nym-node.service- You can also do
service <NODE> stoporservice <NODE> restart.
Anytime you make any changes to your systemd script after you’ve enabled it, you will need to run:
systemctl daemon-reload
service nym-node restart
This lets your operating system know it’s ok to reload the service configuration and restarts the node in a graceful way.
Routing Configuration
We recommend operators to configure their nym-node with the full routing configuration.
However, most of the time the packets sent through the Mixnet are IPv4 based. The IPv6 packets are still pretty rare and therefore it’s not mandatory from operational point of view to have this configuration implemented if you running only mixnode mode.
If you preparing to run a nym-node with all modes enabled in the future, this setup is required.
Networking configuration across different ISPs and various operation systems does not have a generic solution. If the provided configuration setup doesn’t solve your problem check out IPv6 troubleshooting page. Be aware that you may have to do more research, customised adjustments or contact your ISP to change settings for your VPS.
Network Tunnel Manager (network-tunnel-manager.sh, NTM) is currently the one tool handling the configuration of nym-node hosting server, according to the required design (node’s functionality, WireGuard setup etc).
NTM cand administrate these areas:
-
IPv4 and IPv6 routing to the internet
-
The
nymtun0interface (Mixnet / 5-hop): dynamically managed by theexit-gatewayservice. When the service is stopped,nymtun0disappears, and when started,nymtun0is recreated. -
The
nymwginterface (WG / 2-hop): used for creating a secure wireguard tunnel as part of the Nym Network configuration. -
iptablesrules specific tonymwgto ensure proper routing and forwarding through the wireguard tunnel. Thenymwginterface needs to be correctly configured and active for the related commands to function properly. This includes applying or removing iptables rules and running connectivity tests through thenymwgtunnel. -
WireGuard exit policy: Mixnet uses a common exit policy , to apply the same for WG, the operators need to set that one up on their server using
iptablesrules. -
Testing and validating all above
Before starting with the following configuration, make sure you have the latest nym-node binary installed and your VPS setup finished properly!
Run the following steps as root!
Choose configuration command according your setup
New nym-node full configuration
This design is meant for operators setting up a new node on a fresh machine and it will result with a complete server readiness for routing as Entry Gateway and Exit Gateway in both Mixnet and WireGuard mode.
Download network-tunnel-manager.sh, make executable and run with --help command:
curl -L https://raw.githubusercontent.com/nymtech/nym/refs/heads/develop/scripts/nym-node-setup/network-tunnel-manager.sh -o network-tunnel-manager.sh && \
chmod +x network-tunnel-manager.sh && \
./network-tunnel-manager.sh --help
Make sure your nym-node service is up and running and bonded
- If you setting up a new node and not upgrading an existing one, keep it running and bond your node now! Then come back here and follow the rest of the configuration.
Run command for configuration:
- Nodes with WireGuard enabled: Configures interfaces (
nymtun0andnymwg), IPv4 and IPv6 routing, WireGuard exit policy and does validation tests
./network-tunnel-manager.sh complete_networking_configuration- Nodes with WireGuard disabled: Does everything like the command above without WireGuard exit policy
./network-tunnel-manager.sh nym_tunnel_setup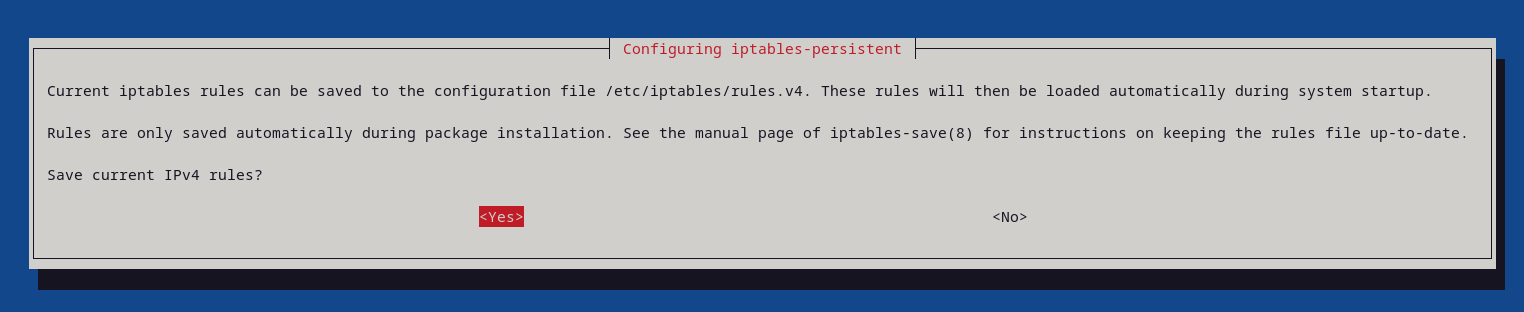
Note that the functionality the node runs in is decided by arguments on the node itself / in node’s config.toml, this tool only prepares the server.
Make sure that you get the validation of all connectivity. If there are still any problems, please refer to troubleshooting section.
If you moved your nym-node from one server to another, please re-do routing configuration by running NTM and QUIC helpers.
Quick IPv6 Check
IPv6 routing is not only a case for gateways. Imagine a rare occasion when you run a mixnode without IPv6 enabled and a client will sent IPv6 packets through the Mixnet through such route:
[client] -> [entry-gateway] -> [mixnode layer 1] -> [your mixnode] -> [IPv6 mixnode layer3] -> [exit-gateway]In this (unusual) case your mixnode will not be able to route the packets. The node will drop the packets and its performance would go down. For that reason it’s beneficial to have IPv6 enabled when running a mixnode functionality.
You can always check IPv6 address and connectivity by using some of these methods:
# locally listed IPv6 addresses
ip -6 addr
# globally reachable IPv6 addresses
ip -6 addr show scope global
# with DNS
dig -6 TXT +short o-o.myaddr.l.google.com @ns1.google.com
dig -t aaaa +short myip.opendns.com @resolver1.opendns.com
# https check
curl -6 https://ifconfig.co
curl -6 https://ipv6.icanhazip.com
# using telnet
telnet -6 ipv6.telnetmyip.comMake sure to keep your IPv4 address enabled while setting up IPv6, as the majority of routing goes through that one!
Wireguard Exit Policy Configuration
In case you had used network-tunnel-manager.sh with the command complete_networking_setup, your WireGuard exit policy is already setup. You can test it in the next chapter.
Nym Node running as Exit Gateway has contains multiple modules, one of them is Nym Network Requester(NR), routing TCP traffic to the internet. To make sure that the node is not just an open proxy, NR checks agains Nym exit policy following these conditions (in this exact order):
- Do we explicitly block those IP addresses regardless of ports?
- Do we allow those specific ports regardless of IPs?
- Do block EVERYTHING else!
The exit policy is same for all NRs, the content is shaped by an offchain governance of Nym Node operators on our forum .
There is a caveat though. NR is only routing TCP streams and therefore any other type of routing than Mixnet is not filtered thorugh the exit policy. To ensure that Nym Nodes follow the same exit policy when routing IP packets through WireGuard and don’t act as open proxies, the operators have to set up these rules via IP tables rules.
For all routing configuration we provide one tool network-tunnel-manager.sh (NTM). This tool manages WireGuard exit policy as well.
In case you haven’t run network-tunnel-manager.sh with the command complete_networking_setup you need to use NTM for WireGuard exit policy configuration.
Folow these steps
Run the following steps as root!
Download network-tunnel-manager.sh, make executable and run with --help command:
curl -L https://raw.githubusercontent.com/nymtech/nym/refs/heads/develop/scripts/nym-node-setup/network-tunnel-manager.sh -o network-tunnel-manager.sh && \
chmod +x network-tunnel-manager.sh && \
./network-tunnel-manager.sh --helpInstall exit policy
- Clear old rules and configure new ones:
./network-tunnel-manager.sh exit_policy_clear
./network-tunnel-manager.sh exit_policy_install- The output should look like this:
iptables-persistent is already installed.
Configuring IP forwarding...
net.ipv6.conf.all.forwarding=1
net.ipv4.ip_forward=1
net.ipv6.conf.all.forwarding = 1
net.ipv4.ip_forward = 1
IP forwarding configured successfully.
Creating Nym exit policy chain...
Chain NYM-EXIT already exists. Flushing it...
Chain NYM-EXIT already exists in ip6tables. Flushing it...
NYM-EXIT all opt -- in * out nymwg 0.0.0.0/0 -> 0.0.0.0/0
NYM-EXIT all opt in * out nymwg ::/0 -> ::/0
Setting up NAT rules...
MASQUERADE all opt -- in * out ens3 0.0.0.0/0 -> 0.0.0.0/0
IPv4 NAT rule already exists.
MASQUERADE all opt in * out ens3 ::/0 -> ::/0
IPv6 NAT rule already exists.
ACCEPT all opt -- in nymwg out ens3 0.0.0.0/0 -> 0.0.0.0/0
ACCEPT all opt -- in ens3 out nymwg 0.0.0.0/0 -> 0.0.0.0/0 state RELATED,ESTABLISHED
ACCEPT all opt in nymwg out ens3 ::/0 -> ::/0
ACCEPT all opt in ens3 out nymwg ::/0 -> ::/0 state RELATED,ESTABLISHED
Configuring DNS and ICMP rules...
ACCEPT icmp opt -- in * out * 0.0.0.0/0 -> 0.0.0.0/0 icmptype 8
ACCEPT icmp opt -- in * out * 0.0.0.0/0 -> 0.0.0.0/0 icmptype 0
ACCEPT icmpv6 opt in * out * ::/0 -> ::/0
ACCEPT udp opt -- in * out * 0.0.0.0/0 -> 0.0.0.0/0 udp dpt:53
ACCEPT tcp opt -- in * out * 0.0.0.0/0 -> 0.0.0.0/0 tcp dpt:53
ACCEPT udp opt in * out * ::/0 -> ::/0 udp dpt:53
ACCEPT tcp opt in * out * ::/0 -> ::/0 tcp dpt:53
Applying Spamhaus blocklist...
Downloading exit policy from https://nymtech.net/.wellknown/network-requester/exit-policy.txt
Processing 429 blocklist rules...
REJECT all opt -- in * out * 0.0.0.0/0 -> 205.189.71.0/24 reject-with icmp-port-unreachable
REJECT all opt -- in * out * 0.0.0.0/0 -> 205.189.72.0/23 reject-with icmp-port-unreachable
Blocklist applied successfully.
Applying allowed ports...
Adding rules for SILC (Port: 706)
Added: NYM-EXIT tcp port 706
Added: NYM-EXIT tcp port 706
Added: NYM-EXIT udp port 706
Added: NYM-EXIT udp port 706
Adding rules for PostgreSQL (Port: 5432)
Added: NYM-EXIT tcp port 5432
Added: NYM-EXIT tcp port 5432
Added: NYM-EXIT udp port 5432
Added: NYM-EXIT udp port 5432
Adding rules for CPanel (Port: 2082-2083)
Added: NYM-EXIT tcp port range 2082:2083
Added: NYM-EXIT tcp port range 2082:2083
Added: NYM-EXIT udp port range 2082:2083
Added: NYM-EXIT udp port range 2082:2083
Adding rules for Zcash (Port: 8232-8233)
Added: NYM-EXIT tcp port range 8232:8233
Added: NYM-EXIT tcp port range 8232:8233
Added: NYM-EXIT udp port range 8232:8233
Added: NYM-EXIT udp port range 8232:8233
Adding rules for VLSILicenseManager (Port: 1500)
Added: NYM-EXIT tcp port 1500
Added: NYM-EXIT tcp port 1500
Added: NYM-EXIT udp port 1500
Added: NYM-EXIT udp port 1500
Adding rules for NTP (Port: 123)
Added: NYM-EXIT tcp port 123
Added: NYM-EXIT tcp port 123
Added: NYM-EXIT udp port 123
Added: NYM-EXIT udp port 123
Adding rules for PKTKRB (Port: 1293)
Added: NYM-EXIT tcp port 1293
Added: NYM-EXIT tcp port 1293
Added: NYM-EXIT udp port 1293
Added: NYM-EXIT udp port 1293
Adding rules for OpenPGP (Port: 11371)
Added: NYM-EXIT tcp port 11371
Added: NYM-EXIT tcp port 11371
Added: NYM-EXIT udp port 11371
Added: NYM-EXIT udp port 11371
Adding rules for HTTPS (Port: 443)
Added: NYM-EXIT tcp port 443
Added: NYM-EXIT tcp port 443
Added: NYM-EXIT udp port 443
Added: NYM-EXIT udp port 443
Adding rules for POP3 (Port: 110)
Added: NYM-EXIT tcp port 110
Added: NYM-EXIT tcp port 110
Added: NYM-EXIT udp port 110
Added: NYM-EXIT udp port 110
Adding rules for OpenVPN (Port: 1194)
Added: NYM-EXIT tcp port 1194
Added: NYM-EXIT tcp port 1194
Added: NYM-EXIT udp port 1194
Added: NYM-EXIT udp port 1194
Adding rules for XboxLive (Port: 3074)
Added: NYM-EXIT tcp port 3074
Added: NYM-EXIT tcp port 3074
Added: NYM-EXIT udp port 3074
Added: NYM-EXIT udp port 3074
Adding rules for OracleDB (Port: 1521)
Added: NYM-EXIT tcp port 1521
Added: NYM-EXIT tcp port 1521
Added: NYM-EXIT udp port 1521
Added: NYM-EXIT udp port 1521
Adding rules for NFS (Port: 2049)
Added: NYM-EXIT tcp port 2049
Added: NYM-EXIT tcp port 2049
Added: NYM-EXIT udp port 2049
Added: NYM-EXIT udp port 2049
Adding rules for Kerberos (Port: 88)
Added: NYM-EXIT tcp port 88
Added: NYM-EXIT tcp port 88
Added: NYM-EXIT udp port 88
Added: NYM-EXIT udp port 88
Adding rules for POP3OverTLS (Port: 995)
Added: NYM-EXIT tcp port 995
Added: NYM-EXIT tcp port 995
Added: NYM-EXIT udp port 995
Added: NYM-EXIT udp port 995
Adding rules for DarkFiTor (Port: 25551)
Added: NYM-EXIT tcp port 25551
Added: NYM-EXIT tcp port 25551
Added: NYM-EXIT udp port 25551
Added: NYM-EXIT udp port 25551
Adding rules for MMCC (Port: 5050)
Added: NYM-EXIT tcp port 5050
Added: NYM-EXIT tcp port 5050
Added: NYM-EXIT udp port 5050
Added: NYM-EXIT udp port 5050
Adding rules for WHOIS (Port: 43)
Added: NYM-EXIT tcp port 43
Added: NYM-EXIT tcp port 43
Added: NYM-EXIT udp port 43
Added: NYM-EXIT udp port 43
Adding rules for NetnewsAdmin (Port: 991)
Added: NYM-EXIT tcp port 991
Added: NYM-EXIT tcp port 991
Added: NYM-EXIT udp port 991
Added: NYM-EXIT udp port 991
Adding rules for IMAP (Port: 143)
Added: NYM-EXIT tcp port 143
Added: NYM-EXIT tcp port 143
Added: NYM-EXIT udp port 143
Added: NYM-EXIT udp port 143
Adding rules for AndroidMarket (Port: 5228)
Added: NYM-EXIT tcp port 5228
Added: NYM-EXIT tcp port 5228
Added: NYM-EXIT udp port 5228
Added: NYM-EXIT udp port 5228
Adding rules for SMBWindowsFileShare (Port: 445)
Added: NYM-EXIT tcp port 445
Added: NYM-EXIT tcp port 445
Added: NYM-EXIT udp port 445
Added: NYM-EXIT udp port 445
Adding rules for RTSPAlt (Port: 1755)
Added: NYM-EXIT tcp port 1755
Added: NYM-EXIT tcp port 1755
Added: NYM-EXIT udp port 1755
Added: NYM-EXIT udp port 1755
Adding rules for IMAPOverTLS (Port: 993)
Added: NYM-EXIT tcp port 993
Added: NYM-EXIT tcp port 993
Added: NYM-EXIT udp port 993
Added: NYM-EXIT udp port 993
Adding rules for TorORPort (Port: 9001)
Added: NYM-EXIT tcp port 9001
Added: NYM-EXIT tcp port 9001
Added: NYM-EXIT udp port 9001
Added: NYM-EXIT udp port 9001
Adding rules for XMPP (Port: 5222-5223)
Added: NYM-EXIT tcp port range 5222:5223
Added: NYM-EXIT tcp port range 5222:5223
Added: NYM-EXIT udp port range 5222:5223
Added: NYM-EXIT udp port range 5222:5223
Adding rules for FTP (Port: 20-21)
Added: NYM-EXIT tcp port range 20:21
Added: NYM-EXIT tcp port range 20:21
Added: NYM-EXIT udp port range 20:21
Added: NYM-EXIT udp port range 20:21
Adding rules for MOSH (Port: 60000-61000)
Added: NYM-EXIT tcp port range 60000:61000
Added: NYM-EXIT tcp port range 60000:61000
Added: NYM-EXIT udp port range 60000:61000
Added: NYM-EXIT udp port range 60000:61000
Adding rules for Zephyr (Port: 2102-2104)
Added: NYM-EXIT tcp port range 2102:2104
Added: NYM-EXIT tcp port range 2102:2104
Added: NYM-EXIT udp port range 2102:2104
Added: NYM-EXIT udp port range 2102:2104
Adding rules for Rsync (Port: 873)
Added: NYM-EXIT tcp port 873
Added: NYM-EXIT tcp port 873
Added: NYM-EXIT udp port 873
Added: NYM-EXIT udp port 873
Adding rules for Steam (Port: 27000-27050)
Added: NYM-EXIT tcp port range 27000:27050
Added: NYM-EXIT tcp port range 27000:27050
Added: NYM-EXIT udp port range 27000:27050
Added: NYM-EXIT udp port range 27000:27050
Adding rules for Git (Port: 9418)
Added: NYM-EXIT tcp port 9418
Added: NYM-EXIT tcp port 9418
Added: NYM-EXIT udp port 9418
Added: NYM-EXIT udp port 9418
Adding rules for MSNP (Port: 1863)
Added: NYM-EXIT tcp port 1863
Added: NYM-EXIT tcp port 1863
Added: NYM-EXIT udp port 1863
Added: NYM-EXIT udp port 1863
Adding rules for SimplifyMedia (Port: 8087-8088)
Added: NYM-EXIT tcp port range 8087:8088
Added: NYM-EXIT tcp port range 8087:8088
Added: NYM-EXIT udp port range 8087:8088
Added: NYM-EXIT udp port range 8087:8088
Adding rules for TorDirPort (Port: 9030)
Added: NYM-EXIT tcp port 9030
Added: NYM-EXIT tcp port 9030
Added: NYM-EXIT udp port 9030
Added: NYM-EXIT udp port 9030
Adding rules for Virtuozzo (Port: 4643)
Added: NYM-EXIT tcp port 4643
Added: NYM-EXIT tcp port 4643
Added: NYM-EXIT udp port 4643
Added: NYM-EXIT udp port 4643
Adding rules for Gaming (Port: 9339)
Added: NYM-EXIT tcp port 9339
Added: NYM-EXIT tcp port 9339
Added: NYM-EXIT udp port 9339
Added: NYM-EXIT udp port 9339
Adding rules for VMware (Port: 902-904)
Added: NYM-EXIT tcp port range 902:904
Added: NYM-EXIT tcp port range 902:904
Added: NYM-EXIT udp port range 902:904
Added: NYM-EXIT udp port range 902:904
Adding rules for Sametime (Port: 1533)
Added: NYM-EXIT tcp port 1533
Added: NYM-EXIT tcp port 1533
Added: NYM-EXIT udp port 1533
Added: NYM-EXIT udp port 1533
Adding rules for NBX (Port: 2095-2096)
Added: NYM-EXIT tcp port range 2095:2096
Added: NYM-EXIT tcp port range 2095:2096
Added: NYM-EXIT udp port range 2095:2096
Added: NYM-EXIT udp port range 2095:2096
Adding rules for ICQ (Port: 5190)
Added: NYM-EXIT tcp port 5190
Added: NYM-EXIT tcp port 5190
Added: NYM-EXIT udp port 5190
Added: NYM-EXIT udp port 5190
Adding rules for KerberosAdmin (Port: 749)
Added: NYM-EXIT tcp port 749
Added: NYM-EXIT tcp port 749
Added: NYM-EXIT udp port 749
Added: NYM-EXIT udp port 749
Adding rules for RWHOIS (Port: 4321)
Added: NYM-EXIT tcp port 4321
Added: NYM-EXIT tcp port 4321
Added: NYM-EXIT udp port 4321
Added: NYM-EXIT udp port 4321
Adding rules for NDMP (Port: 10000)
Added: NYM-EXIT tcp port 10000
Added: NYM-EXIT tcp port 10000
Added: NYM-EXIT udp port 10000
Added: NYM-EXIT udp port 10000
Adding rules for DNS (Port: 53)
Added: NYM-EXIT tcp port 53
Added: NYM-EXIT tcp port 53
Added: NYM-EXIT udp port 53
Added: NYM-EXIT udp port 53
Adding rules for GoogleVoice (Port: 19294)
Added: NYM-EXIT tcp port 19294
Added: NYM-EXIT tcp port 19294
Added: NYM-EXIT udp port 19294
Added: NYM-EXIT udp port 19294
Adding rules for IMAP3 (Port: 220)
Added: NYM-EXIT tcp port 220
Added: NYM-EXIT tcp port 220
Added: NYM-EXIT udp port 220
Added: NYM-EXIT udp port 220
Adding rules for Bitcoin (Port: 8332-8333)
Added: NYM-EXIT tcp port range 8332:8333
Added: NYM-EXIT tcp port range 8332:8333
Added: NYM-EXIT udp port range 8332:8333
Added: NYM-EXIT udp port range 8332:8333
Adding rules for Mumble (Port: 64738)
Added: NYM-EXIT tcp port 64738
Added: NYM-EXIT tcp port 64738
Added: NYM-EXIT udp port 64738
Added: NYM-EXIT udp port 64738
Adding rules for DarkFi (Port: 26661)
Added: NYM-EXIT tcp port 26661
Added: NYM-EXIT tcp port 26661
Added: NYM-EXIT udp port 26661
Added: NYM-EXIT udp port 26661
Adding rules for PPTP (Port: 1723)
Added: NYM-EXIT tcp port 1723
Added: NYM-EXIT tcp port 1723
Added: NYM-EXIT udp port 1723
Added: NYM-EXIT udp port 1723
Adding rules for HTTPSALT (Port: 8443)
Added: NYM-EXIT tcp port 8443
Added: NYM-EXIT tcp port 8443
Added: NYM-EXIT udp port 8443
Added: NYM-EXIT udp port 8443
Adding rules for HTTPProxy (Port: 8888)
Added: NYM-EXIT tcp port 8888
Added: NYM-EXIT tcp port 8888
Added: NYM-EXIT udp port 8888
Added: NYM-EXIT udp port 8888
Adding rules for GNUnet (Port: 2086-2087)
Added: NYM-EXIT tcp port range 2086:2087
Added: NYM-EXIT tcp port range 2086:2087
Added: NYM-EXIT udp port range 2086:2087
Added: NYM-EXIT udp port range 2086:2087
Adding rules for Lightning (Port: 9735)
Added: NYM-EXIT tcp port 9735
Added: NYM-EXIT tcp port 9735
Added: NYM-EXIT udp port 9735
Added: NYM-EXIT udp port 9735
Adding rules for RTSP (Port: 554)
Added: NYM-EXIT tcp port 554
Added: NYM-EXIT tcp port 554
Added: NYM-EXIT udp port 554
Added: NYM-EXIT udp port 554
Adding rules for DNSOverTLS (Port: 853)
Added: NYM-EXIT tcp port 853
Added: NYM-EXIT tcp port 853
Added: NYM-EXIT udp port 853
Added: NYM-EXIT udp port 853
Adding rules for SSH (Port: 22)
Added: NYM-EXIT tcp port 22
Added: NYM-EXIT tcp port 22
Added: NYM-EXIT udp port 22
Added: NYM-EXIT udp port 22
Adding rules for Electrum (Port: 8082)
Added: NYM-EXIT tcp port 8082
Added: NYM-EXIT tcp port 8082
Added: NYM-EXIT udp port 8082
Added: NYM-EXIT udp port 8082
Adding rules for TelnetOverTLS (Port: 992)
Added: NYM-EXIT tcp port 992
Added: NYM-EXIT tcp port 992
Added: NYM-EXIT udp port 992
Added: NYM-EXIT udp port 992
Adding rules for Minecraft (Port: 25565)
Added: NYM-EXIT tcp port 25565
Added: NYM-EXIT tcp port 25565
Added: NYM-EXIT udp port 25565
Added: NYM-EXIT udp port 25565
Adding rules for SVN (Port: 3690)
Added: NYM-EXIT tcp port 3690
Added: NYM-EXIT tcp port 3690
Added: NYM-EXIT udp port 3690
Added: NYM-EXIT udp port 3690
Adding rules for Kpasswd (Port: 464)
Added: NYM-EXIT tcp port 464
Added: NYM-EXIT tcp port 464
Added: NYM-EXIT udp port 464
Added: NYM-EXIT udp port 464
Adding rules for MoneroRPC (Port: 18089)
Added: NYM-EXIT tcp port 18089
Added: NYM-EXIT tcp port 18089
Added: NYM-EXIT udp port 18089
Added: NYM-EXIT udp port 18089
Adding rules for RemoteHTTPS (Port: 981)
Added: NYM-EXIT tcp port 981
Added: NYM-EXIT tcp port 981
Added: NYM-EXIT udp port 981
Added: NYM-EXIT udp port 981
Adding rules for Tari (Port: 9053)
Added: NYM-EXIT tcp port 9053
Added: NYM-EXIT tcp port 9053
Added: NYM-EXIT udp port 9053
Added: NYM-EXIT udp port 9053
Adding rules for ElectrumSSL (Port: 50002)
Added: NYM-EXIT tcp port 50002
Added: NYM-EXIT tcp port 50002
Added: NYM-EXIT udp port 50002
Added: NYM-EXIT udp port 50002
Adding rules for HTTPSALT2 (Port: 9443)
Added: NYM-EXIT tcp port 9443
Added: NYM-EXIT tcp port 9443
Added: NYM-EXIT udp port 9443
Added: NYM-EXIT udp port 9443
Adding rules for LDAP (Port: 389)
Added: NYM-EXIT tcp port 389
Added: NYM-EXIT tcp port 389
Added: NYM-EXIT udp port 389
Added: NYM-EXIT udp port 389
Adding rules for HTTP (Port: 80-81)
Added: NYM-EXIT tcp port range 80:81
Added: NYM-EXIT tcp port range 80:81
Added: NYM-EXIT udp port range 80:81
Added: NYM-EXIT udp port range 80:81
Adding rules for MongoDBDefault (Port: 27017)
Added: NYM-EXIT tcp port 27017
Added: NYM-EXIT tcp port 27017
Added: NYM-EXIT udp port 27017
Added: NYM-EXIT udp port 27017
Adding rules for RTPVOIP (Port: 5000-5005)
Added: NYM-EXIT tcp port range 5000:5005
Added: NYM-EXIT tcp port range 5000:5005
Added: NYM-EXIT udp port range 5000:5005
Added: NYM-EXIT udp port range 5000:5005
Adding rules for MSSQL (Port: 1433)
Added: NYM-EXIT tcp port 1433
Added: NYM-EXIT tcp port 1433
Added: NYM-EXIT udp port 1433
Added: NYM-EXIT udp port 1433
Adding rules for MQTTS (Port: 8883)
Added: NYM-EXIT tcp port 8883
Added: NYM-EXIT tcp port 8883
Added: NYM-EXIT udp port 8883
Added: NYM-EXIT udp port 8883
Adding rules for MySQL (Port: 3306)
Added: NYM-EXIT tcp port 3306
Added: NYM-EXIT tcp port 3306
Added: NYM-EXIT udp port 3306
Added: NYM-EXIT udp port 3306
Adding rules for TeamSpeak (Port: 8767)
Added: NYM-EXIT tcp port 8767
Added: NYM-EXIT tcp port 8767
Added: NYM-EXIT udp port 8767
Added: NYM-EXIT udp port 8767
Adding rules for GroupWise (Port: 1677)
Added: NYM-EXIT tcp port 1677
Added: NYM-EXIT tcp port 1677
Added: NYM-EXIT udp port 1677
Added: NYM-EXIT udp port 1677
Adding rules for Monero (Port: 18080-18081)
Added: NYM-EXIT tcp port range 18080:18081
Added: NYM-EXIT tcp port range 18080:18081
Added: NYM-EXIT udp port range 18080:18081
Added: NYM-EXIT udp port range 18080:18081
Adding rules for EnsimControlPanel (Port: 19638)
Added: NYM-EXIT tcp port 19638
Added: NYM-EXIT tcp port 19638
Added: NYM-EXIT udp port 19638
Added: NYM-EXIT udp port 19638
Adding rules for QTServerAdmin (Port: 1220)
Added: NYM-EXIT tcp port 1220
Added: NYM-EXIT tcp port 1220
Added: NYM-EXIT udp port 1220
Added: NYM-EXIT udp port 1220
Adding rules for Finger (Port: 79)
Added: NYM-EXIT tcp port 79
Added: NYM-EXIT tcp port 79
Added: NYM-EXIT udp port 79
Added: NYM-EXIT udp port 79
Adding rules for FTPOverTLS (Port: 989-990)
Added: NYM-EXIT tcp port range 989:990
Added: NYM-EXIT tcp port range 989:990
Added: NYM-EXIT udp port range 989:990
Added: NYM-EXIT udp port range 989:990
Adding rules for LDAPS (Port: 636)
Added: NYM-EXIT tcp port 636
Added: NYM-EXIT tcp port 636
Added: NYM-EXIT udp port 636
Added: NYM-EXIT udp port 636
Adding default reject rule...
Default reject rule added successfully.
Port allowlist applied successfully.
Saving iptables rules to make them persistent...
Rules saved to /etc/iptables/rules.v4 and /etc/iptables/rules.v6
Nym exit policy installed successfully.Check status of your configuration
./network-tunnel-manager.sh exit_policy_status- The output should look like this:
Nym Exit Policy Status:
----------------------
Network Device: eth0
Wireguard Interface: nymwg
Interface Details:
87: nymwg: <POINTOPOINT,NOARP,UP,LOWER_UP> mtu 1420 qdisc noqueue state UNKNOWN mode DEFAULT group default qlen 1000
link/none
IP Addresses:
87: nymwg: <POINTOPOINT,NOARP,UP,LOWER_UP> mtu 1420 qdisc noqueue state UNKNOWN group default qlen 1000
inet 10.1.0.1/32 brd 10.1.0.1 scope global nymwg
valid_lft forever preferred_lft forever
87: nymwg: <POINTOPOINT,NOARP,UP,LOWER_UP> mtu 1420 qdisc noqueue state UNKNOWN group default qlen 1000
inet6 fc01::1/112 scope global
valid_lft forever preferred_lft forever
Iptables Chains:
IPv4 Chain:
Chain NYM-EXIT (1 references)
pkts bytes target prot opt in out source destination
0 0 REJECT all -- * * 0.0.0.0/0 5.188.10.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 5.188.11.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 31.132.36.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 31.184.237.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 37.9.42.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 43.229.52.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 45.9.148.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 45.43.128.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 45.142.120.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.148.112.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.148.120.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.148.127.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.173.208.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 79.110.22.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.121.39.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.193.75.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.12.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.81.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.82.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.83.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.164.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.216.3.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.220.163.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.200.248.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.243.90.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.243.91.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.243.93.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.234.99.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 103.99.0.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 103.215.80.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 103.239.28.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.166.96.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.207.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.233.0.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.239.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.243.192.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.247.96.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.250.192.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.250.224.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 107.182.112.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 107.190.160.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 141.136.22.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 150.129.40.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 159.174.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 162.222.128.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 162.249.20.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 163.53.247.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 166.117.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 167.74.0.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 167.160.96.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 168.64.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 168.76.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 168.129.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 169.239.152.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 170.114.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 172.98.0.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 174.136.192.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 176.121.14.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.159.97.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.159.100.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.159.107.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.14.192.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.14.193.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.14.195.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.21.8.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.39.8.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.71.0.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.77.248.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.116.172.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.116.175.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.124.56.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.129.8.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.130.36.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.130.40.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.140.53.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.143.220.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.143.222.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.143.223.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.146.168.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.165.153.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.193.90.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.244.29.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.244.30.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.244.31.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 188.247.230.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.26.25.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.31.212.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.43.175.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.43.176.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.43.184.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.161.80.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.251.231.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 193.228.91.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 194.5.97.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 194.5.98.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 194.5.99.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 195.182.57.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 196.45.120.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 196.61.192.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 196.196.8.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 196.199.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 197.231.208.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.20.16.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.45.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.56.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.151.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.151.152.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.178.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.183.32.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.186.25.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.187.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.200.0.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.200.8.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 198.206.140.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.5.152.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.34.128.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.84.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.89.16.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.120.163.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.166.200.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.185.192.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.196.192.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.198.160.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.212.96.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.223.0.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.241.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.249.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.253.224.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 199.254.32.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.19.38.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.44.224.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.52.96.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.87.199.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.107.208.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.126.244.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.130.16.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.147.64.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.232.0.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.144.0.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.148.192.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.151.128.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.159.45.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.172.244.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.189.71.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.189.72.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.203.0.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.233.224.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 205.236.189.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.124.104.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.195.224.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.197.165.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.209.80.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.224.160.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.226.0.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.226.32.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 206.227.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 207.22.192.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 207.45.224.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 207.110.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 207.110.128.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 209.66.128.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 216.179.128.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 217.8.116.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 217.8.117.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 223.169.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 223.254.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 42.4.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 68.119.232.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 68.215.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 69.244.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 70.111.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 70.126.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 112.78.2.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 195.20.40.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 14.160.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 27.2.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 27.106.108.128/25 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 37.236.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.100.21.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 39.32.0.0/11 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 41.190.2.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 41.190.30.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 45.116.232.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.118.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.161.9.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 60.184.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 62.44.134.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 78.85.40.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 79.11.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 79.108.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 81.93.93.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 83.24.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 83.149.19.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 84.18.126.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.198.140.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.116.176.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.227.224.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.241.88.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 89.114.108.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.196.250.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 93.122.192.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 95.0.60.160/27 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 95.110.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 89.189.152.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 103.26.246.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 106.51.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.124.0.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.124.16.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.126.128.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.175.6.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 111.125.108.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 112.101.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.80.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.128.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 114.96.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 114.115.128.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 115.72.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 118.20.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.24.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 125.167.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 139.5.157.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 146.185.223.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 154.68.4.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 177.55.154.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 177.125.30.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 177.224.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.135.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 179.5.103.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 181.67.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 181.174.101.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 182.69.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 182.160.100.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 182.184.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 182.253.162.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 183.82.128.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 183.128.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.36.88.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.150.15.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 185.172.86.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 186.179.100.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 189.216.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 190.235.110.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 190.239.190.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.64.121.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 193.34.141.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 193.188.254.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 197.229.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 201.148.126.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 202.136.88.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 200.121.192.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 220.164.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 221.228.192.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 24.0.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 27.184.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.0.0.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 58.53.128.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 59.92.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 60.52.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 60.176.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 60.215.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 61.163.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 62.194.131.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 64.175.32.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 67.116.236.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 67.121.120.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 67.124.36.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 68.62.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 69.112.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 71.56.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 76.112.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 78.97.32.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 80.108.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 81.240.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 82.72.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 82.169.28.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 84.127.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 84.144.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 84.220.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.48.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.54.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.85.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.86.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.176.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 89.217.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.176.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.182.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 92.0.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 92.112.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 92.128.0.0/12 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.128.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 110.212.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 111.85.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 112.224.0.0/11 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.70.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.89.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.111.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.224.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 113.240.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 114.246.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 114.248.80.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 115.60.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 115.213.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 116.238.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 117.22.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 117.136.0.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 118.80.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 118.168.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 120.0.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 120.68.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 121.29.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 122.169.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 122.173.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.67.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.101.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.112.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.134.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.161.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.174.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.188.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 123.244.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 124.89.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 124.128.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 124.134.0.0/17 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 124.94.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 125.93.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 125.125.176.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 125.224.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 150.70.75.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 166.204.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.191.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.125.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 183.91.2.0/23 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 183.184.0.0/13 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 188.23.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 188.98.0.0/15 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 189.64.0.0/14 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 201.53.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 201.82.64.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 212.56.64.0/18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 218.202.219.0/24 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 220.152.128.0/22 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 220.178.0.0/19 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 221.11.32.0/20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 222.183.0.0/16 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 222.240.216.0/21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 82.165.159.132/31 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 91.208.144.164 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 209.182.193.155 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 213.205.38.29 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 5.79.71.205 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 5.79.71.225 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.129.41 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.129.213 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.144.42 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.147.11 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.151.95 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.153.71 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.153.115 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.168.194 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.169.101 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.170.84 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.174.35 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.179.9 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.182.164 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.184.75 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.186.110 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.186.114 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.188.186 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 38.229.191.189 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 46.244.21.4 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 50.21.181.152 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 50.63.202.35 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 52.5.245.208 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 64.71.166.50 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 64.71.188.178 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 67.215.255.139 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 74.200.48.169 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 74.208.153.9 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 74.208.164.166 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 74.208.64.191 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.17.31.122 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 85.17.31.82 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.18.146 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.149.145 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.149.153 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.18.112 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.18.141 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.190.153 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.190.154 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.190.157 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.20.192 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.24.200 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.253.18 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 87.106.26.9 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 95.211.230.75 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.42.225.122 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 104.244.14.252 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 109.70.26.37 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 144.217.74.156 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 146.148.124.166 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 148.81.111.111 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 151.80.148.103 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 176.58.104.168 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.162.203.202 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.162.203.211 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.162.203.226 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 178.162.217.107 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 184.105.76.250 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 184.105.192.2 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.0.72.20 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.0.72.21 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.169.69.25 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.42.116.41 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 192.42.119.41 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 193.166.255.170 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 193.166.255.171 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 204.11.56.48 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 208.91.197.46 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 212.227.20.93 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 212.227.20.116 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 212.227.20.164 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 213.165.83.176 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 216.218.135.114 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 216.218.185.162 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 216.218.208.114 reject-with icmp-port-unreachable
0 0 REJECT all -- * * 0.0.0.0/0 216.66.15.109 reject-with icmp-port-unreachable
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:706
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:706
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:5432
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:5432
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:2082:2083
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:2082:2083
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:8232:8233
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:8232:8233
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1500
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1500
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:123
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:123
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1293
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1293
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:11371
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:11371
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:443
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:443
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:110
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:110
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1194
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1194
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:3074
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:3074
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1521
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1521
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:2049
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:2049
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:88
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:88
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:995
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:995
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:25551
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:25551
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:5050
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:5050
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:43
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:43
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:991
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:991
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:143
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:143
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:5228
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:5228
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:445
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:445
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1755
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1755
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:993
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:993
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9001
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9001
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:5222:5223
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:5222:5223
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:20:21
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:20:21
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:60000:61000
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:60000:61000
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:2102:2104
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:2102:2104
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:873
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:873
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:27000:27050
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:27000:27050
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9418
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9418
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1863
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1863
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:8087:8088
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:8087:8088
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9030
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9030
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:4643
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:4643
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9339
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9339
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:902:904
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:902:904
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1533
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1533
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:2095:2096
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:2095:2096
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:5190
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:5190
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:749
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:749
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:4321
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:4321
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:10000
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:10000
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:53
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:53
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:19294
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:19294
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:220
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:220
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:8332:8333
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:8332:8333
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:64738
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:64738
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:26661
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:26661
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1723
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1723
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:8443
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:8443
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:8888
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:8888
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:2086:2087
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:2086:2087
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9735
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9735
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:554
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:554
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:853
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:853
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:22
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:22
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:8082
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:8082
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:992
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:992
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:25565
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:25565
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:3690
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:3690
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:464
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:464
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:18089
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:18089
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:981
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:981
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9053
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9053
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:50002
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:50002
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:9443
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:9443
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:389
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:389
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:80:81
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:80:81
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:27017
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:27017
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:5000:5005
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:5000:5005
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1433
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1433
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:8883
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:8883
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:3306
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:3306
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:8767
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:8767
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1677
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1677
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:18080:18081
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:18080:18081
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:19638
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:19638
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:1220
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:1220
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:79
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:79
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpts:989:990
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpts:989:990
0 0 ACCEPT tcp -- * * 0.0.0.0/0 0.0.0.0/0 tcp dpt:636
0 0 ACCEPT udp -- * * 0.0.0.0/0 0.0.0.0/0 udp dpt:636
0 0 REJECT all -- * * 0.0.0.0/0 0.0.0.0/0 reject-with icmp-port-unreachable
IPv6 Chain:
Chain NYM-EXIT (1 references)
pkts bytes target prot opt in out source destination
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:706
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:706
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:5432
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:5432
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:2082:2083
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:2082:2083
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:8232:8233
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:8232:8233
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1500
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1500
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:123
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:123
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1293
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1293
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:11371
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:11371
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:443
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:443
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:110
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:110
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1194
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1194
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:3074
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:3074
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1521
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1521
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:2049
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:2049
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:88
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:88
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:995
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:995
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:25551
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:25551
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:5050
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:5050
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:43
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:43
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:991
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:991
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:143
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:143
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:5228
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:5228
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:445
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:445
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1755
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1755
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:993
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:993
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9001
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9001
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:5222:5223
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:5222:5223
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:20:21
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:20:21
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:60000:61000
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:60000:61000
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:2102:2104
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:2102:2104
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:873
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:873
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:27000:27050
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:27000:27050
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9418
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9418
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1863
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1863
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:8087:8088
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:8087:8088
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9030
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9030
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:4643
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:4643
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9339
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9339
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:902:904
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:902:904
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1533
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1533
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:2095:2096
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:2095:2096
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:5190
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:5190
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:749
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:749
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:4321
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:4321
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:10000
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:10000
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:53
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:53
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:19294
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:19294
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:220
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:220
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:8332:8333
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:8332:8333
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:64738
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:64738
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:26661
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:26661
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1723
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1723
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:8443
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:8443
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:8888
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:8888
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:2086:2087
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:2086:2087
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9735
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9735
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:554
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:554
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:853
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:853
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:22
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:22
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:8082
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:8082
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:992
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:992
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:25565
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:25565
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:3690
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:3690
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:464
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:464
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:18089
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:18089
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:981
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:981
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9053
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9053
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:50002
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:50002
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:9443
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:9443
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:389
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:389
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:80:81
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:80:81
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:27017
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:27017
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:5000:5005
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:5000:5005
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1433
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1433
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:8883
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:8883
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:3306
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:3306
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:8767
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:8767
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1677
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1677
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:18080:18081
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:18080:18081
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:19638
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:19638
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:1220
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:1220
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:79
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:79
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpts:989:990
0 0 ACCEPT udp * * ::/0 ::/0 udp dpts:989:990
0 0 ACCEPT tcp * * ::/0 ::/0 tcp dpt:636
0 0 ACCEPT udp * * ::/0 ::/0 udp dpt:636
0 0 REJECT all * * ::/0 ::/0 reject-with icmp6-port-unreachable
IP Forwarding:
IPv4: 1
IPv6: 1Now your WireGuard routing (2-hop) should have same rotuing permissions like Nym exit policy used on 5-hop (Mixnet) mode of NymVPN.
Testing Wireguard Exit Policy
For all routing configuration we provide one tool network-tunnel-manager.sh (NTM). This tool manages WireGuard tests all configurations, including WireGuard exit policy as well.
You can use NTM to validate the application of the IP tables routes on your nym-node by checking it from the server side as well as from the outside.
From the server
Make sure to have the latest NTM:
curl -L https://raw.githubusercontent.com/nymtech/nym/refs/heads/develop/scripts/nym-node-setup/network-tunnel-manager.sh -o network-tunnel-manager.sh && \
chmod +x network-tunnel-manager.sh && \
./network-tunnel-manager.sh --helpRun tests with NTM
./network-tunnel-manager.sh exit_policy_test_connectivity
./network-tunnel-manager.sh exit_policy_tests- The output should look like this:
Running Nym Exit Policy Verification Tests...
Testing Port Range Rules...
Testing FTP tcp port range 20-21
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:20:21
✓ Rule exists: NYM-EXIT tcp port range 20:21
Testing HTTP tcp port range 80-81
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:80:81
✓ Rule exists: NYM-EXIT tcp port range 80:81
Testing CPanel tcp port range 2082-2083
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:2082:2083
✓ Rule exists: NYM-EXIT tcp port range 2082:2083
Testing XMPP tcp port range 5222-5223
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:5222:5223
✓ Rule exists: NYM-EXIT tcp port range 5222:5223
Testing Steam (sampling) tcp port range 27000-27050
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:27000:27050
✓ Rule exists: NYM-EXIT tcp port range 27000:27050
Testing FTP over TLS tcp port range 989-990
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:989:990
✓ Rule exists: NYM-EXIT tcp port range 989:990
Testing RTP/VoIP tcp port range 5000-5005
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:5000:5005
✓ Rule exists: NYM-EXIT tcp port range 5000:5005
Testing Simplify Media tcp port range 8087-8088
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:8087:8088
✓ Rule exists: NYM-EXIT tcp port range 8087:8088
Testing Zcash tcp port range 8232-8233
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:8232:8233
✓ Rule exists: NYM-EXIT tcp port range 8232:8233
Testing Bitcoin tcp port range 8332-8333
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:8332:8333
✓ Rule exists: NYM-EXIT tcp port range 8332:8333
Testing Monero tcp port range 18080-18081
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpts:18080:18081
✓ Rule exists: NYM-EXIT tcp port range 18080:18081
Test test_port_range_rules PASSED
Testing Critical Service Rules...
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpt:22
✓ Rule exists: NYM-EXIT tcp port 22
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpt:53
✓ Rule exists: NYM-EXIT tcp port 53
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpt:443
✓ Rule exists: NYM-EXIT tcp port 443
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpt:853
✓ Rule exists: NYM-EXIT tcp port 853
ACCEPT  tcp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   tcp dpt:1194
✓ Rule exists: NYM-EXIT tcp port 1194
ACCEPT  udp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   udp dpt:53
✓ Rule exists: NYM-EXIT udp port 53
ACCEPT  udp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   udp dpt:123
✓ Rule exists: NYM-EXIT udp port 123
ACCEPT  udp opt -- in * out *  0.0.0.0/0  -> 0.0.0.0/0   udp dpt:1194
✓ Rule exists: NYM-EXIT udp port 1194
Relevant existing rules for HTTP (port 80):
Test test_critical_services PASSED
This test takes some time, do not quit the process

Testing Default Reject Rule...
✓ Default REJECT rule exists
Test test_default_reject_rule PASSED

Test Summary:
Total Tests:     3
Failures:        0
All Tests Passed Successfully!
Optionally you can do some manual sanity checks
- Run this command to define variable
BLOCKED_IPand try topingit:
BLOCKED_IP=$(grep "ExitPolicy reject" /etc/nym/exit-policy.txt | head -1 | sed -E 's/ExitPolicy reject ([^:]+):.*/\1/' | sed 's/\/.*$//')

ping -c 3 $BLOCKED_IP- You should see
100% packet lossas an outcome.
telnet $BLOCKED_IP 80- You should see
telnet: Unable to connect to remote host: Connection timed out.
If all works , your node has successfully implemented WireGuard exit policy with the same routing permissions like Nym exit policy used on 5-hop (Mixnet) for TCP routing.
QUIC Transport Bridge Deployment
QUIC bridge is a requirement for all nodes which enable Wireguard functionality. Note that it this feature is compatible with nodes from v1.19.0 (platform release v2025.18-jarlsberg) and newer!
Nym Network uses various transport bridges for routing the packets. Right now operators need to configure our implementation of general-purpose transport layer network protocol called QUIC .
Operators can use Nym Bridge Configuration Tool and compile the Bridge Runner binary themselves.
We recommend a more convenient QUIC bridge deployment using a script quic_bridge_deployment.sh, following the steps below.
This script assumes that you follow the convention of running a nym-node as root. In case you run as a non-root user, please follow manual QUIC bridge setup and ask for support in the Matrix channel .
Download quic_bridge_deployment.sh script
- SSH to your server
- Run as root
- Download the script and make executable
curl -L https://raw.githubusercontent.com/nymtech/nym/refs/heads/develop/scripts/nym-node-setup/quic_bridge_deployment.sh -o quic_bridge_deployment.sh && \
chmod +x quic_bridge_deployment.sh
Run the script with full_bridge_setup command
- Optional: open
tmuxin case you will need to run another commands on the VPS - Run the script with a command
full_bridge_setup
./quic_bridge_deployment.sh full_bridge_setup- If you prefer a non-interactive mode, run the command with this variable (and skip next step):
NONINTERACTIVE=1 ./quic_bridge_deployment.sh full_bridge_setupFollow the interactive prompts
- Make sure you don’t just press enter to insert default values if your setup is different, for example in case of path to the config file
Validate
- After running the script, ensure that the bridges are running correctly:
systemctl status nym-bridge.serviceRestart nym-node service
- When done with the deployment, please restart your node systemd service
service nym-node restart && journalctl -u nym-node.service -f --allCongratulation, you deployed QUIC transport bridge! The script offers a standalone tweaks and checks, you can always run it without any argument to see all the options:
./quic_bridge_deployment.shroot@localhost:~# ./quic_bridge_deployment.sh
Logs are being saved locally to: /var/log/nym-bridge-helper.log
These logs never leave your machine.
Usage: ./quic_bridge_deployment.sh [command]
Commands:
full_bridge_setup - Run full setup
install_bridge_binary - Install nym-bridge (.deb; falls back to source build if libc too old)
install_bridge_cfg_tool - Install bridge-cfg (prebuilt; falls back to source build if libc too old)
run_bridge_cfg_generate - Generate bridges.toml
create_bridge_service - Setup systemd service (respects .deb-provided service)
adjust_ip_forwarding - Enable forwarding
apply_bridge_iptables_rules - NAT rules
configure_dns_and_icmp - Allow ICMP/DNS
------------------------------------------
Script exited with errors (code: 1).
Check the log at: /var/log/nym-bridge-helper.log
------------------------------------------Fixing Metadata Port Showing Not Open in Probe Results
If you have followed the steps outlined above, but the metadata port is not shown as open in either the Node Status API’s probe results or an explorer that gets its data from the API, see below:
Run as root
Confirm correct config.toml private IPv4 address
Ensure that in your config.toml file, this value is set to the default one - any other value here will cause the metadata endpoint to fail:
# Private IP address of the wireguard gateway.
# default: '10.1.0.1'
private_ipv4 = '10.1.0.1'
Then restart your node.
Open the needed port
Run this command if not already done:
ufw allow in on nymwg to any port 51830 proto tcpCheck if the port is open with:
iptables -S | grep 51830Then ensure the metadata endpoint is listening from the correct address with:
netstat -an | egrep LISTEN | egrep "51830"Validate the setup
Once the Node Status API has run a probe on your node, the probe results will reflect this - can_query_metadata_v4 will have true as a value.
The quickest way to check this is by using the NymVPN API and checking the same field:
Running nym-node as a non-root
Some operators prefer to run nym-node without root privileges. It’s possible but still nym-node binary needs higher privileges for network-level operations demanding these permissions. Below is a guide how to go about such setup:
Copying nodes database and the .nym/ directories from /root/.nym to /home/<USER>/.nym/ should be treated as experimental, therefore we would advise this section for operators starting new nodes, rather than tweaking an existing one. We will publish a detailed guide for changing permissions of an existing node soon.
Setup a new user
- Define a variable
user_nameusing your desired user name:
user_name="<USER>"- Run:
user_home="/home/$user_name"

if ! id "$user_name" &>/dev/null; then
    sudo adduser --home "$user_home" --disabled-login --gecos "" "$user_name"
else
    echo "user $user_name already exists"
fi- And follow by:
sudo usermod -aG sudo "$user_name"- Optional: Add to sudoers group:
echo "$user_name ALL=(ALL) NOPASSWD:ALL" | sudo tee -a /etc/sudoers.d/$user_nameGrant needed permissions for network-level operations
While nym-node will be set as a user process, it requires higher privileges for network-level operations, set them up with this command:
sudo setcap 'cap_net_bind_service=+ep cap_net_admin=+ep' nym-nodeAfter replacing or upgrading the binary, you must reapply these permissions each time!
Edit service config file
-
Add these new lines to your
/etc/systemd/system/nym-node.serviceservice config fileAfter=network.targetGroup=<USER>Type=simple
-
Your service file will then look like this:
[Unit]
Description=Nym Node
After=network.target
StartLimitInterval=350
StartLimitBurst=10

[Service]
User=<USER>
Group=<USER>
Type=simple
LimitNOFILE=65536
ExecStart=<PATH>/nym-node run <ARGUMENTS> # add all the flags you use to run your node
KillSignal=SIGINT
Restart=on-failure
RestartSec=30

[Install]
WantedBy=multi-user.target
Reload and restart the service
systemctl daemon-reload && service nym-node restart- If you want to follow the logs, run:
journalctl -u nym-node -fNext Steps
There are a few more good suggestions for nym-node configuration, like Web Secure Socket or Reversed Proxy setup. These are optional and you can skip them if you want. Visit Proxy configuration page to see the guides.